# Beats reporting on Kibana as Standalone Cluster
**URL:** https://discuss.elastic.co/t/beats-reporting-on-kibana-as-standalone-cluster/240711
**Category:** Beats
**Tags:** elastic-stack-monitoring, filebeat
**Created:** [July 10, 2020, 2:06pm UTC](https://discuss.elastic.co/t/beats-reporting-on-kibana-as-standalone-cluster/240711 "2020-07-10T14:06:30Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@vishakh](https://discuss.elastic.co/u/vishakh)
#### Post date: [July 10, 2020, 2:06pm UTC](https://discuss.elastic.co/t/beats-reporting-on-kibana-as-standalone-cluster/240711/1 "2020-07-10T14:06:30Z")
ELK-Stack: 7.8
Beats -\> Logstash -\> ES
in my cluster: I'm ingesting both data logs and monitoring stats to same cluster.
Installed and configured Filebeat 7.8 on a linux server with the below configuration.
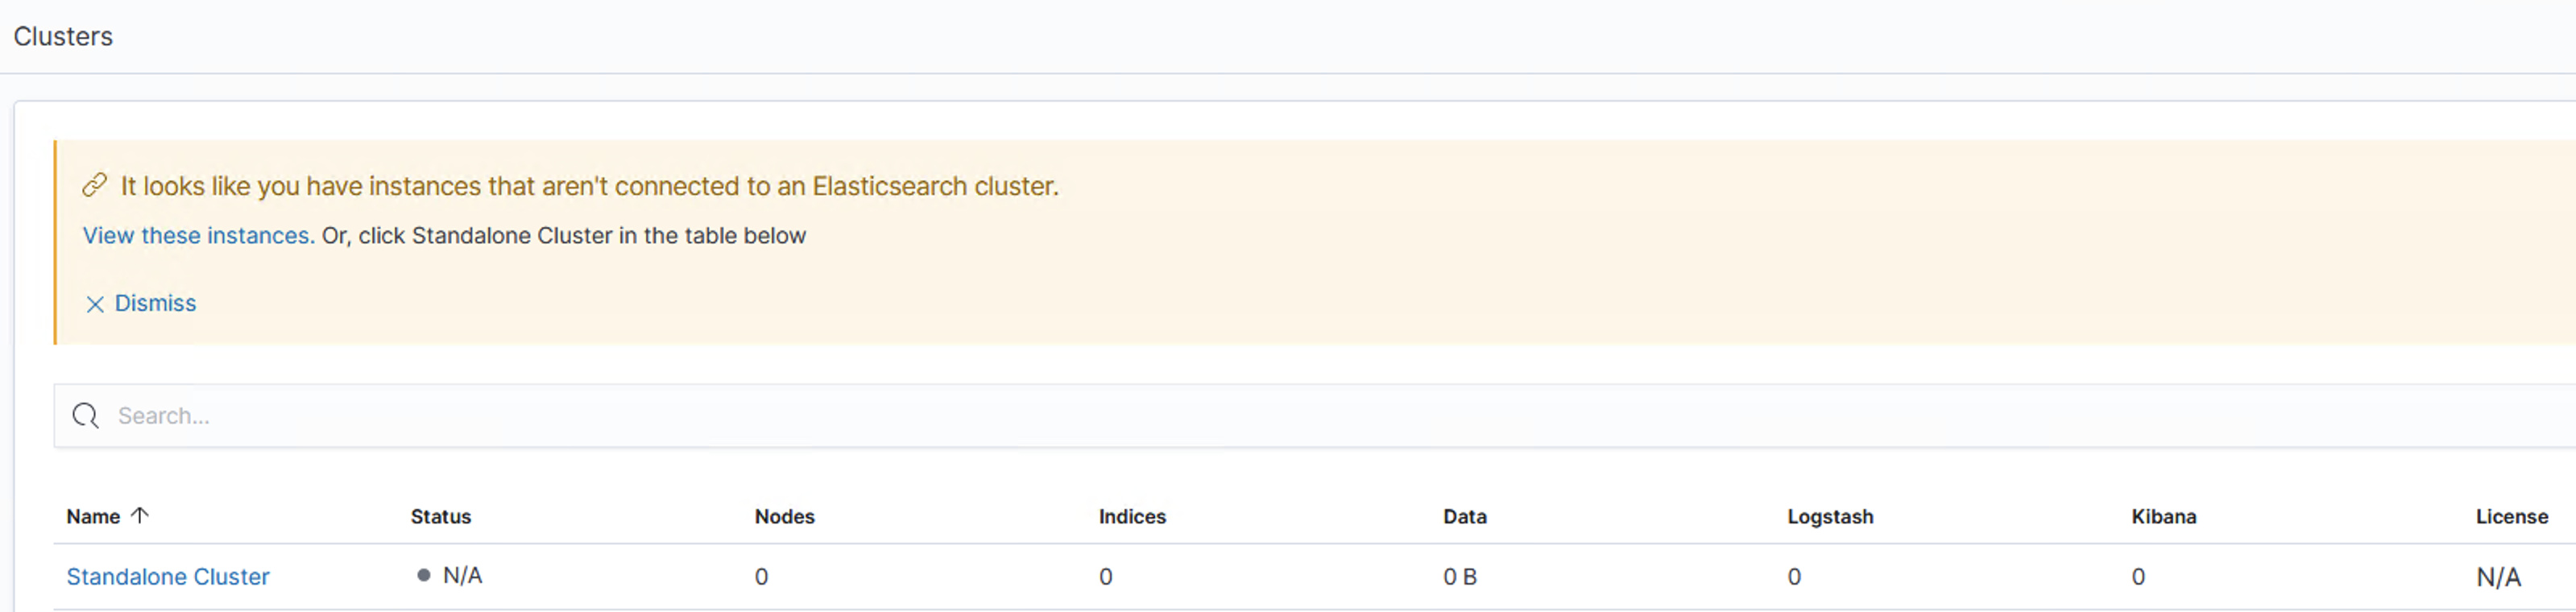
Once started the agent, filebeat-agent is showing/reporting as a new cluster-joinee ("S **tandalone Cluster** ) on kibana as below screenshots.
This new installed beats is not being included under our current cluster's beats section rather it's trying to create a new standalone cluster
Please advise
```auto
# ============================== Filebeat inputs ===============================
filebeat.inputs:
- type: log
enabled: false
paths:
- /var/log/yum.log
# ============================== Filebeat modules ==============================
filebeat.config.modules:
path: ${path.config}/modules.d/*.yml
reload.enabled: false
# ================================= General ===================================
#name:
tags: ["stag"]
fields:
env: testing
# ================================= Dashboards =================================
setup.dashboards.enabled: true
# =================================== Kibana ===================================
setup.kibana:
host: ""
username: "elastic"
password: "${ES_PWD}"
ssl.enabled: true
ssl.verification_mode: full
ssl.certificate_authorities: ["/etc/filebeat/certs/ca.crt"]
# ================================== Outputs ===================================
# ------------------------------ Logstash Output -------------------------------
output.logstash:
hosts: [":5044"]
ssl.certificate_authorities: ["/etc/filebeat/certs/ca.crt"]
loadbalance: false
ssl.verification_mode: full
# ================================== Logging ===================================
name: filebeat
logging.level: info
logging.to_files: true
logging.files:
path: /etc/filebeat/logs
rotateeverybytes: 26214400
keepfiles: 7
logging.json: true
logging.ecs: true
# ================================== Keystore ==================================
keystore.path: "${path.config}/filebeat.keystore"
# ============================= X-Pack Monitoring ==============================
monitoring.enabled: true
monitoring.elasticsearch:
hosts: [":9200"]
username: "beats_system"
password: "${BT_PWD}"
ssl.certificate_authorities: ["/etc/filebeat/certs/ca.crt"]
ssl.verification_mode: full
```
---
### Author:  [@vishakh](https://discuss.elastic.co/u/vishakh)
#### Post date: [July 10, 2020, 2:33pm UTC](https://discuss.elastic.co/t/beats-reporting-on-kibana-as-standalone-cluster/240711/2 "2020-07-10T14:33:38Z")
Resolved my issue by explicitly passing the cluster.uuid in the beats.yml
step-1: Get to know the cluster.uuid using `GET /_cluster/stats`
step-2: In your \*beat.yml file add the line `monitoring.cluster_uuid: ""`
step-3: Restart your beats and now your beats will be reporting to same data-cluster
By default, the most recent version of beats(elasticsearch) assumes that we've two clusters one for data/logs and other for monitoring. So need to explicitly specify as to where beats needs to ingest monitoring stats-metrics
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [August 7, 2020, 4:33pm UTC](https://discuss.elastic.co/t/beats-reporting-on-kibana-as-standalone-cluster/240711/3 "2020-08-07T16:33:41Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.