# EQL query to alert 1 alert per each user
**URL:** https://discuss.elastic.co/t/eql-query-to-alert-1-alert-per-each-user/339539
**Category:** SIEM
**Created:** [July 28, 2023, 11:30am UTC](https://discuss.elastic.co/t/eql-query-to-alert-1-alert-per-each-user/339539 "2023-07-28T11:30:09Z")
**Posts on this page:** 4
**Page:** 1
### Author:  [@yzaritskyi](https://discuss.elastic.co/u/yzaritskyi)
#### Post date: [July 28, 2023, 11:30am UTC](https://discuss.elastic.co/t/eql-query-to-alert-1-alert-per-each-user/339539/1 "2023-07-28T11:30:09Z")
Hello all!
I'd like to create a Rule based on the EQL query that will trigger an alert only once per user.
For example:
The input list of logs is
_user1 ip1_
_user1 ip1_
_user2 ip2_
_user5 ip5_
_user4 ip4_
_user4 ip4_
_user20 ip20_
_user1 ip1_
_user20 ip20_
And I want to create alerts based on that logs to see results like this:
_alert1: user1 ip1_
_alert2: user2 ip2_
_alert3: user4 ip4_
_alert4: user5 ip5_
_alert5: user20 ip20_
I try to detect the user's connection to some websites through DNS logs. This Rule runs every 24 hours, but a user can connect to the service I'm interested in more than 1 time, so I usually get more than 1 alert for the same user.
I tried to implement it using **sequence by** , but it doesn't work:
```auto
sequence by user.name, ?process.name
[network where network.protocol == "dns" and dns.question.name : (" ***", "***")]
[network where true]
```
I would be really glad to hear any suggestions or the entire resolution. Thank you!
---
### Author:  [@spong](https://discuss.elastic.co/u/spong)
#### Post date: [August 1, 2023, 10:11pm UTC](https://discuss.elastic.co/t/eql-query-to-alert-1-alert-per-each-user/339539/2 "2023-08-01T22:11:21Z")
Hey there @yzaritskyi ! 👋
So if you only want one per grouping of `user.name` / `process.name`, you might want to try using a `Threshold Rule` ala:
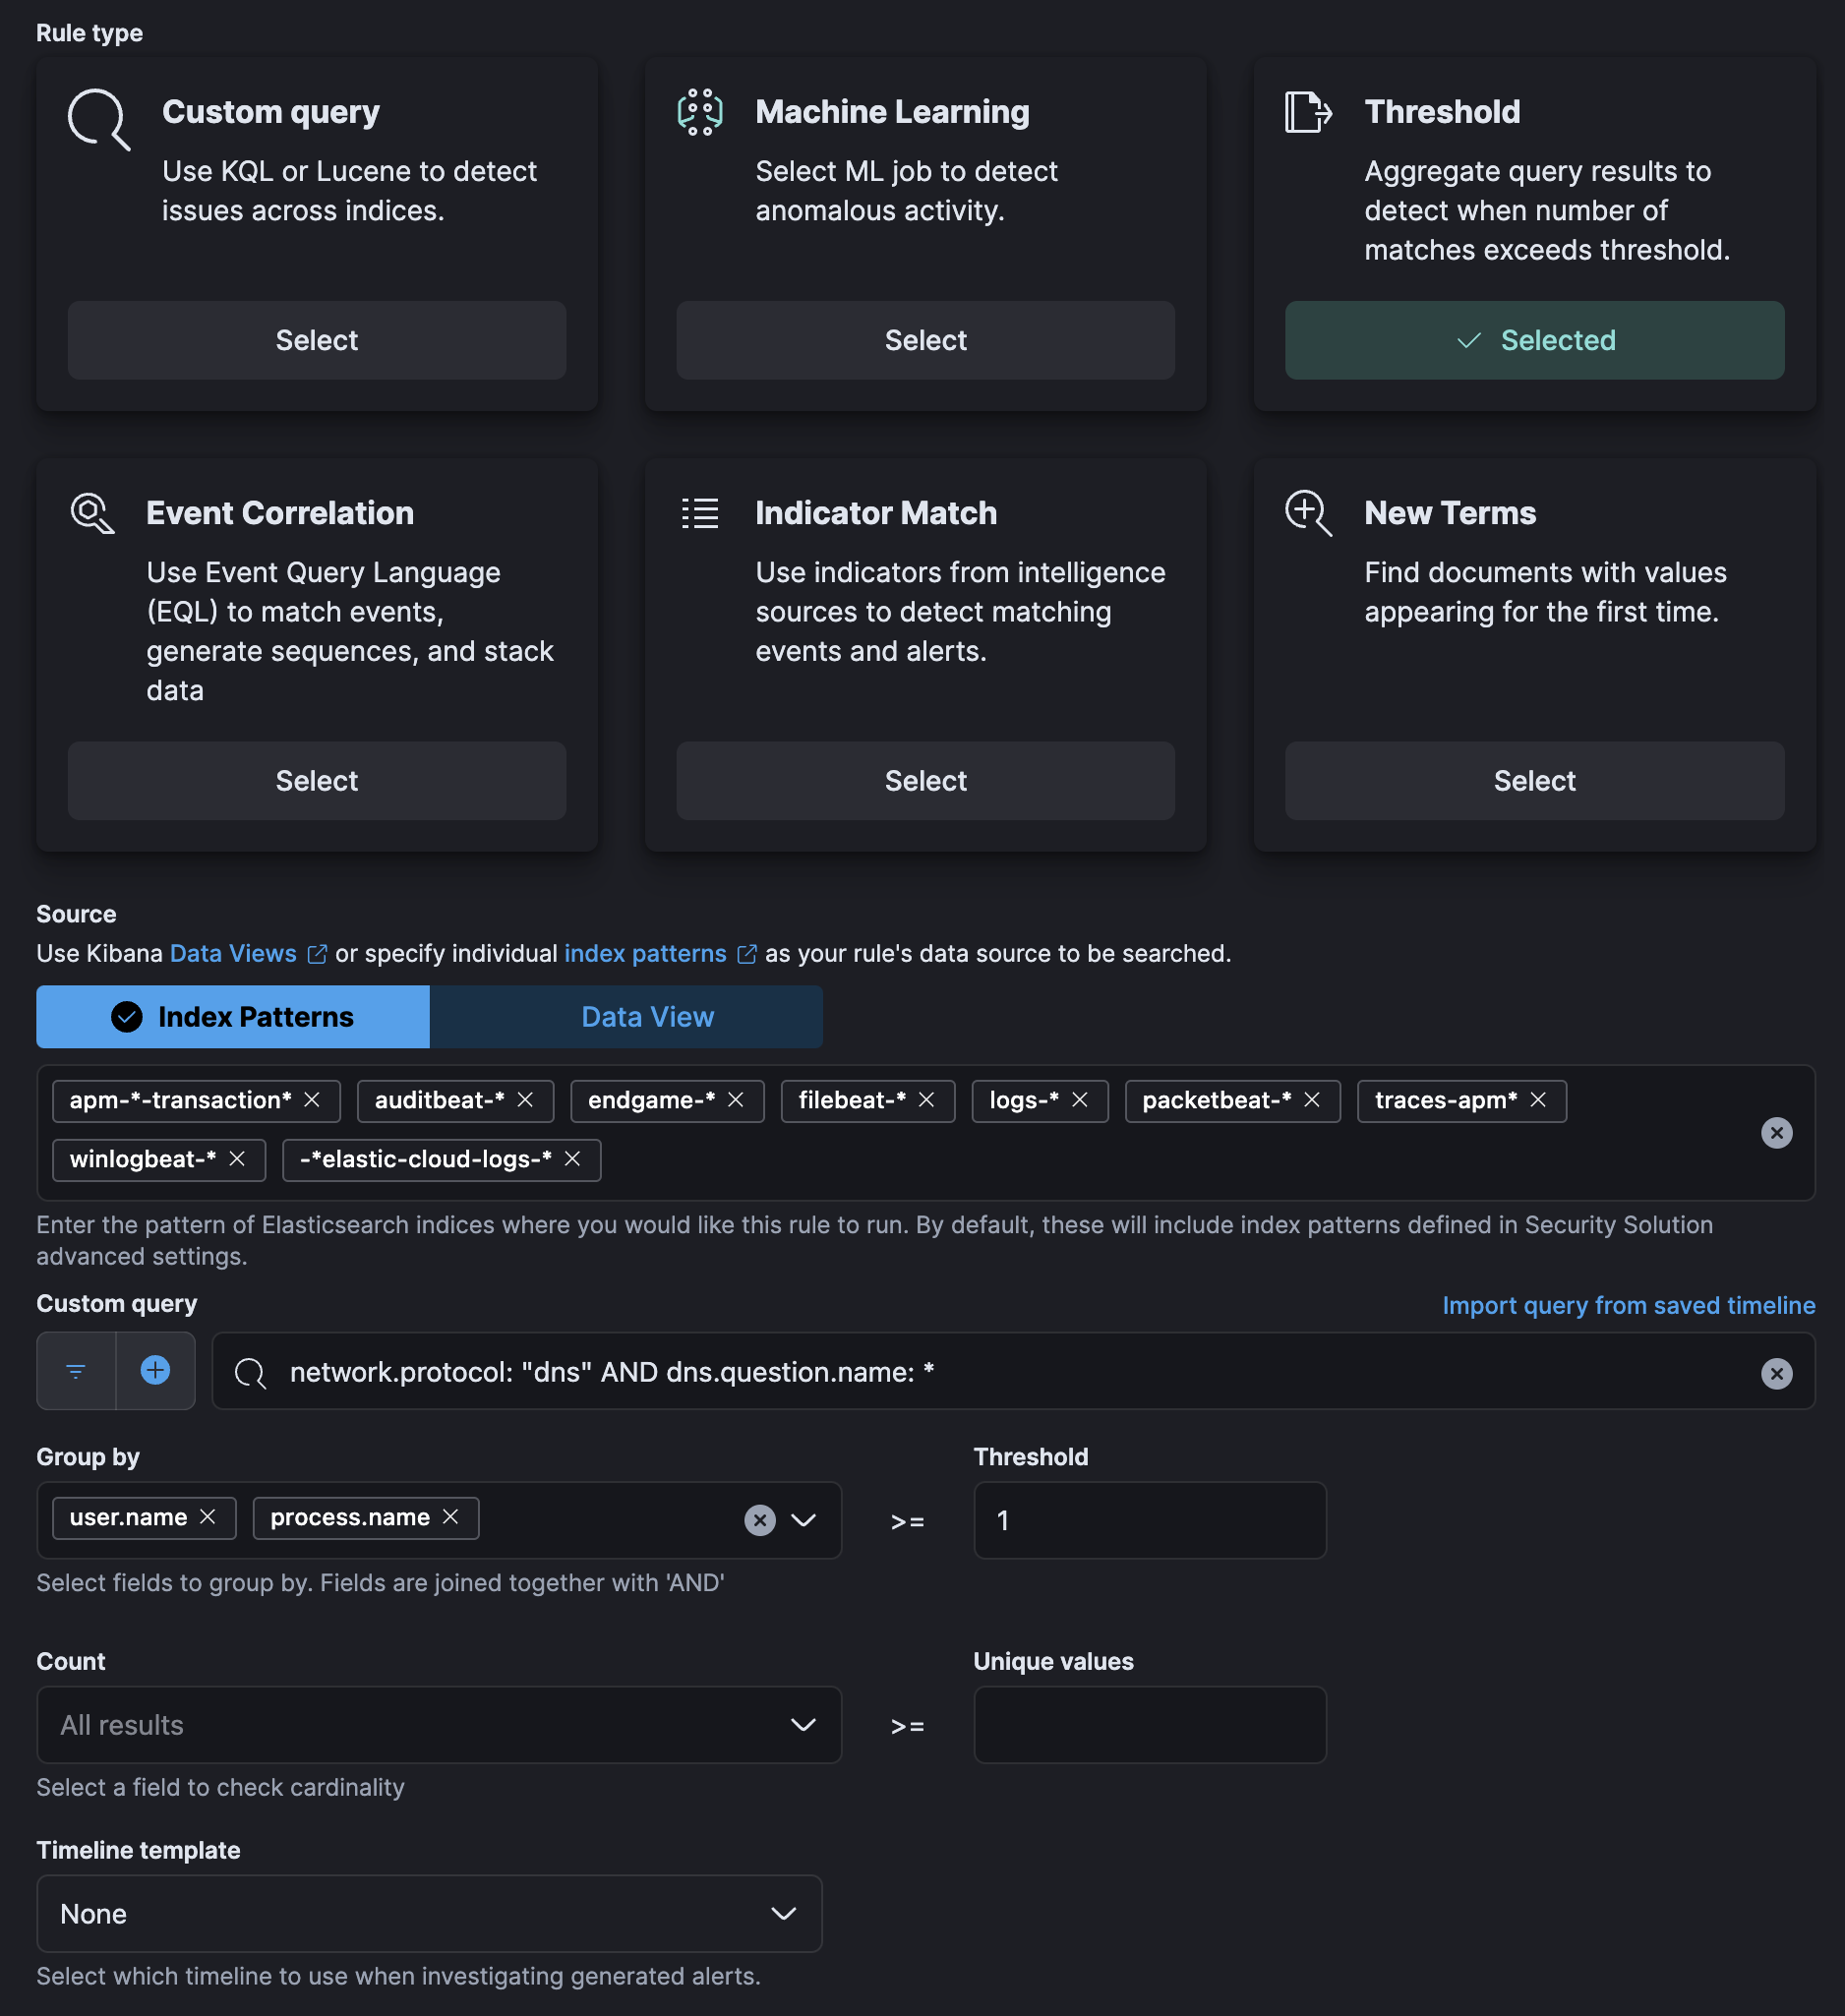
You may want to include the dns name in the `Group by` depending on how you want your alerts broken apart.
Let me know if that works for you!
Cheers!
Garrett
---
### Author:  [@yzaritskyi](https://discuss.elastic.co/u/yzaritskyi)
#### Post date: [August 8, 2023, 1:15pm UTC](https://discuss.elastic.co/t/eql-query-to-alert-1-alert-per-each-user/339539/3 "2023-08-08T13:15:08Z")
Thank you! You helped me a lot! It works exactly how I wanted.
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [September 5, 2023, 1:15pm UTC](https://discuss.elastic.co/t/eql-query-to-alert-1-alert-per-each-user/339539/4 "2023-09-05T13:15:23Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.