# Filebeat/Logstash doesn't send system.auth.\*.\* field data to Elastic Search - v 7.14
**URL:** https://discuss.elastic.co/t/filebeat-logstash-doesnt-send-system-auth-field-data-to-elastic-search-v-7-14/281793
**Category:** Beats
**Tags:** beats-module, filebeat
**Created:** [August 18, 2021, 9:04am UTC](https://discuss.elastic.co/t/filebeat-logstash-doesnt-send-system-auth-field-data-to-elastic-search-v-7-14/281793 "2021-08-18T09:04:21Z")
**Posts on this page:** 4
**Page:** 1
### Author:  [@angheladrianclaudiu](https://discuss.elastic.co/u/angheladrianclaudiu)
#### Post date: [August 18, 2021, 9:04am UTC](https://discuss.elastic.co/t/filebeat-logstash-doesnt-send-system-auth-field-data-to-elastic-search-v-7-14/281793/1 "2021-08-18T09:04:21Z")
I've installed ELK stack with steps described here:
[Current Elastic Release (7.14)](https://www.elastic.co/guide/en/elasticsearch/reference/current/deb.html)
[Current Kibana Release (7.14)](https://www.elastic.co/guide/en/kibana/current/deb.html)
[Current Logstash Release (7.14)](https://www.elastic.co/guide/en/logstash/current/installing-logstash.html#package-repositories)
[Current Filebeat Release (7.14)](https://www.elastic.co/guide/en/beats/filebeat/current/filebeat-installation-configuration.html)
I also used the Logstash configuration presented here with the note under it: [Beats input plugin | Logstash Reference [7.14] | Elastic](https://www.elastic.co/guide/en/logstash/current/plugins-inputs-beats.html#_description_6)
However, after I've run the commands below I couldn't see any data in the loaded dashboards in Kibana:
```auto
sudo filebeat setup --template -E output.logstash.enabled=false -E 'output.elasticsearch.hosts=["localhost:9200"]'
sudo filebeat setup -e -E output.logstash.enabled=false -E output.elasticsearch.hosts=['localhost:9200'] -E setup.kibana.host=localhost:5601
```
It should be something like this:

But it looks like below:

"No results found" is shown in all 4 dashboards: **Syslog | Sudo commands | SSH Logins | New users and groups**
Also, when I tried to lookup data in Discovery and search for system.auth.ssh.events for example I couldn't find anything:
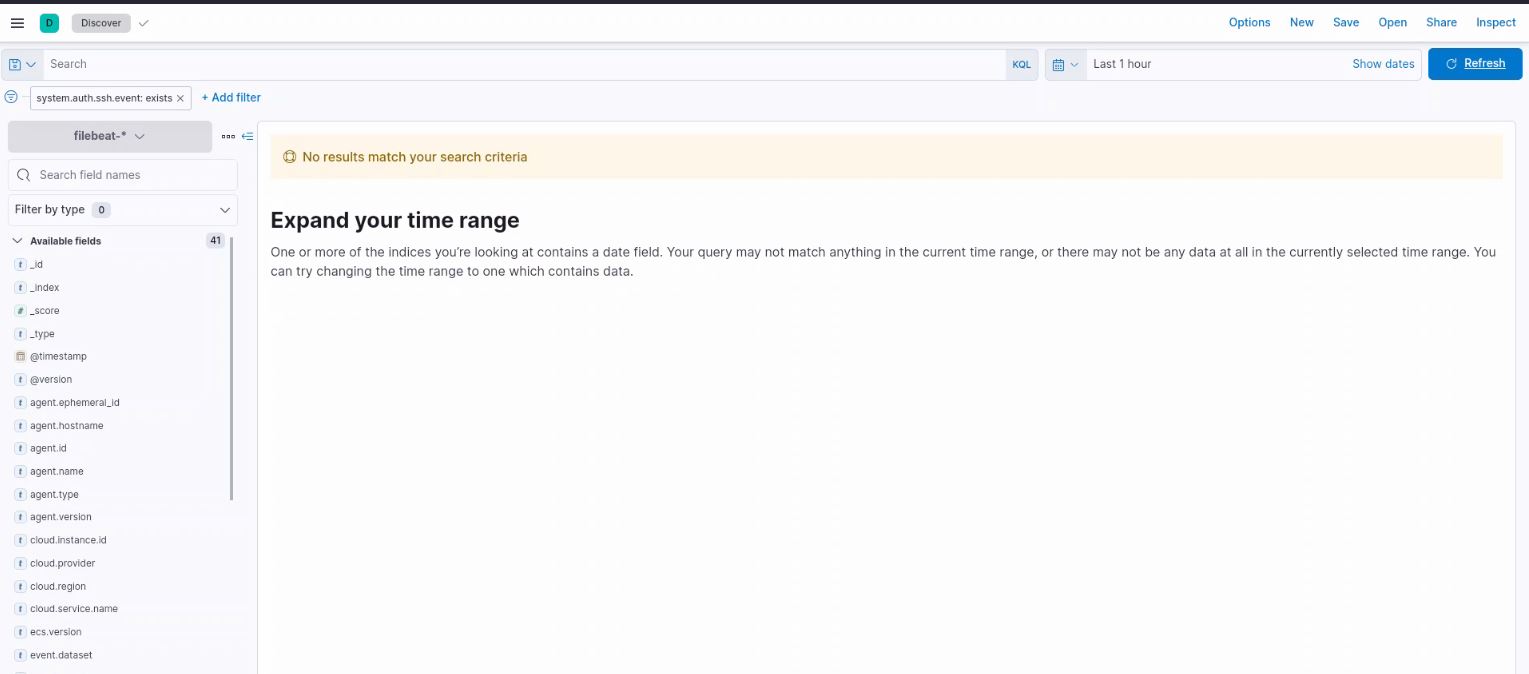
What is the problem?
---
### Author:  [@legoguy1000](https://discuss.elastic.co/u/legoguy1000)
#### Post date: [August 18, 2021, 12:15pm UTC](https://discuss.elastic.co/t/filebeat-logstash-doesnt-send-system-auth-field-data-to-elastic-search-v-7-14/281793/2 "2021-08-18T12:15:30Z")
Did u enable the filebeat system module?? You also need to configure the elasticsearch output when u run setup to load the index template, mappings, and ingest pipelines...
---
### Author:  [@angheladrianclaudiu](https://discuss.elastic.co/u/angheladrianclaudiu)
#### Post date: [August 18, 2021, 3:01pm UTC](https://discuss.elastic.co/t/filebeat-logstash-doesnt-send-system-auth-field-data-to-elastic-search-v-7-14/281793/3 "2021-08-18T15:01:12Z")
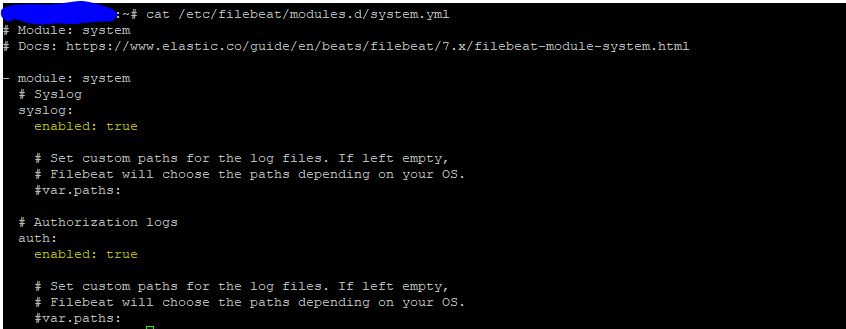
@legoguy1000 Sure. I've enabled the system module and configured logstash to read from filebeat input and send to elasticsearch. Please check below:
```auto
filebeat modules list
```

```auto
cat /etc/filebeat/modules.d/system.yml
```
```auto
cat /etc/logstash/cond.d/beats-input-output.conf
```

These were setup before running the commands in the original post.
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [September 15, 2021, 5:01pm UTC](https://discuss.elastic.co/t/filebeat-logstash-doesnt-send-system-auth-field-data-to-elastic-search-v-7-14/281793/4 "2021-09-15T17:01:33Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.