# How can you enrich and add fields to the correlation event upon rule trigger?
**URL:** https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314
**Category:** Kibana
**Tags:** detection-rules
**Created:** [March 25, 2021, 9:56am UTC](https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314 "2021-03-25T09:56:07Z")
**Posts on this page:** 5
**Page:** 1
### Author:  [@fuzzyWedgie](https://discuss.elastic.co/u/fuzzyWedgie)
#### Post date: [March 25, 2021, 9:56am UTC](https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314/1 "2021-03-25T09:56:07Z")
Hi,
When correlating events I want to do enrichment lookups and add extra fields to the correlation event (signal).
Also we would like to be able to add fields to the correlation event from the source events that cause the trigger or populate some fields hardcoded.
How can we do this? It doesn't seem to be an option in the rules interface and enrichment is only available on ingest?
Enrichment on rule trigger and the ability to add fields on the correlation events seems to me as must haves for any SIEM solution.
---
### Author:  [@jamesspi](https://discuss.elastic.co/u/jamesspi)
#### Post date: [March 27, 2021, 9:24am UTC](https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314/2 "2021-03-27T09:24:36Z")
Hey @fuzzyWedgie ,
I assume you're referring to something similar to Splunk's `lookup` functionality?
> Also we would like to be able to add fields to the correlation event from the source events that cause the trigger or populate some fields hardcoded.
Where do you want to add those, in the action output? All the events from the source fields are included in the output by default. When setting up an external action, you can also add any hardcoded values that you like.
When it comes to enrichment - You can use indicator matching to perform "lookup style" queries. As of our latest version, 7.12 - we now highlight where there was a match and we add that to the output.
If you have a specific use case you're trying to accomplish, I'll be more than happy to help.
Thanks,
James
---
### Author:  [@fuzzyWedgie](https://discuss.elastic.co/u/fuzzyWedgie)
#### Post date: [March 30, 2021, 8:17pm UTC](https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314/3 "2021-03-30T20:17:40Z")
Hey there,
What I would like to do is when a rule meets a certain condition, I want to pull some extra information from a list or some other index to enrich the correlation output. So for example:
Rule trigger: a user logs in on a specific server
--\> lookup the attributes for this user in the user\_index and give me the email-address, phone number, whatever and add these fields to the correlation event (signal).
So no action, I only want to enrich the data in the signal with extra data from another index or just add hardcoded fields and values.
---
### Author:  [@jamesspi](https://discuss.elastic.co/u/jamesspi)
#### Post date: [April 2, 2021, 7:43am UTC](https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314/4 "2021-04-02T07:43:03Z")
Hey @fuzzyWedgie ,
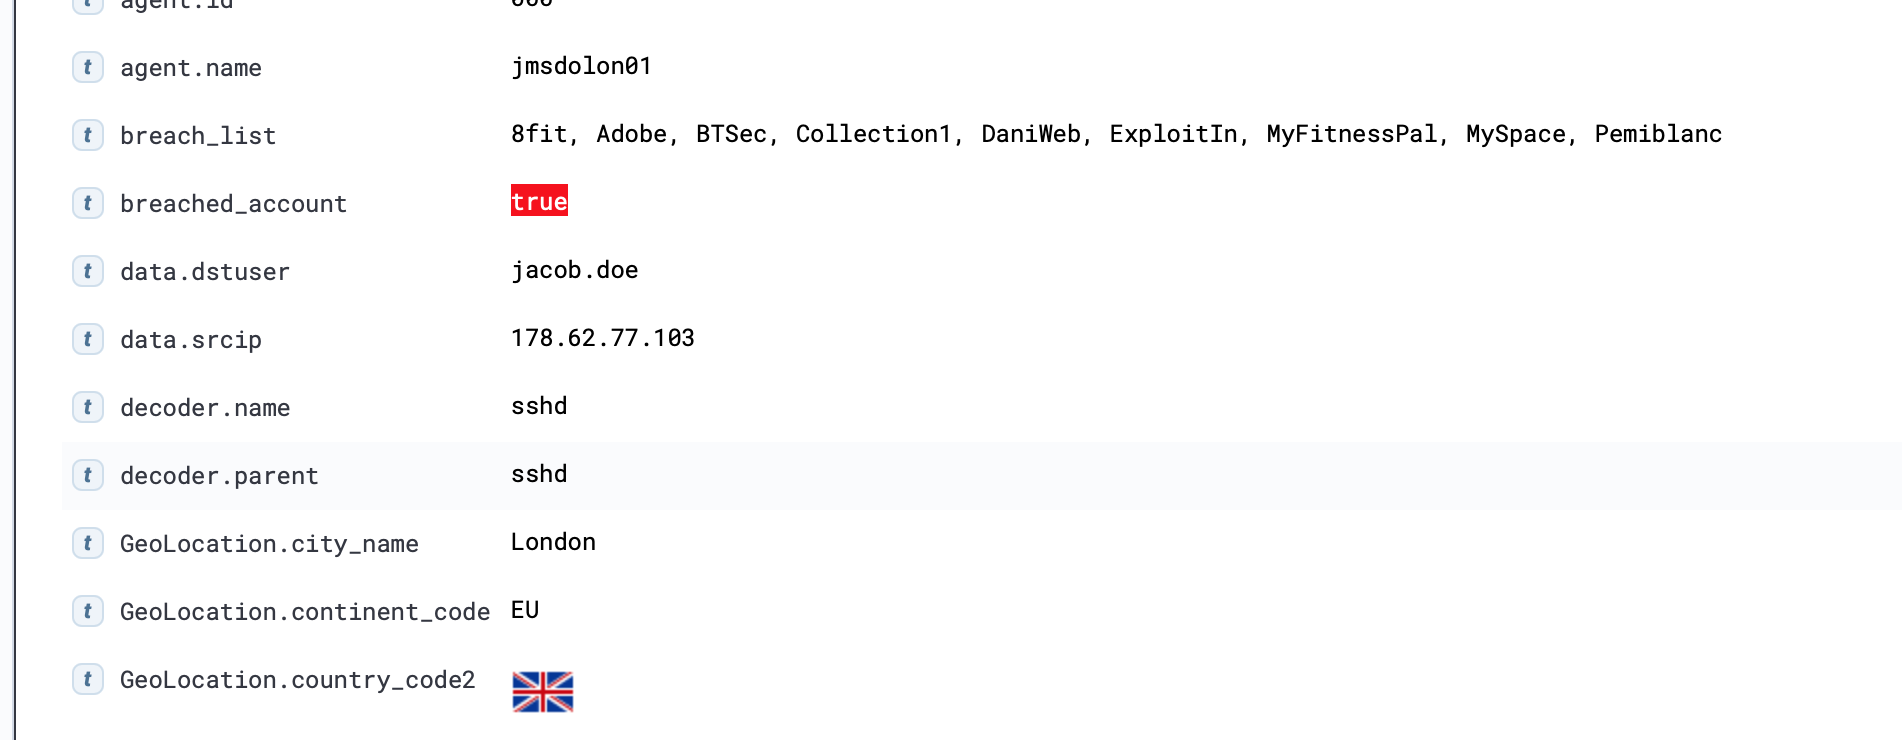
Ok, understood now. Unfortunately there isn't a way to do this on detection today, however, this level of enrichment can be done on ingest. You can enrich events with data from other indices, relation databases, files, REST API results and more. This would mean that you always add the additional events, but, come detection time, it would be a lot more performant because the lookups have already been performed.
I have an example below of some data I enrich on ingest for this purpose. This is an SSH log that I then enrich with the [haveibeenpwned.com](http://haveibeenpwned.com) API and a simulated "vacation" database (which is mysql).
Hope this helps!
James
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [April 30, 2021, 7:44am UTC](https://discuss.elastic.co/t/how-can-you-enrich-and-add-fields-to-the-correlation-event-upon-rule-trigger/268314/5 "2021-04-30T07:44:00Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.