# Kibana 9.1 Security Rule exception edit not possible
**URL:** https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710
**Category:** Kibana
**Created:** [October 14, 2025, 3:06pm UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710 "2025-10-14T15:06:27Z")
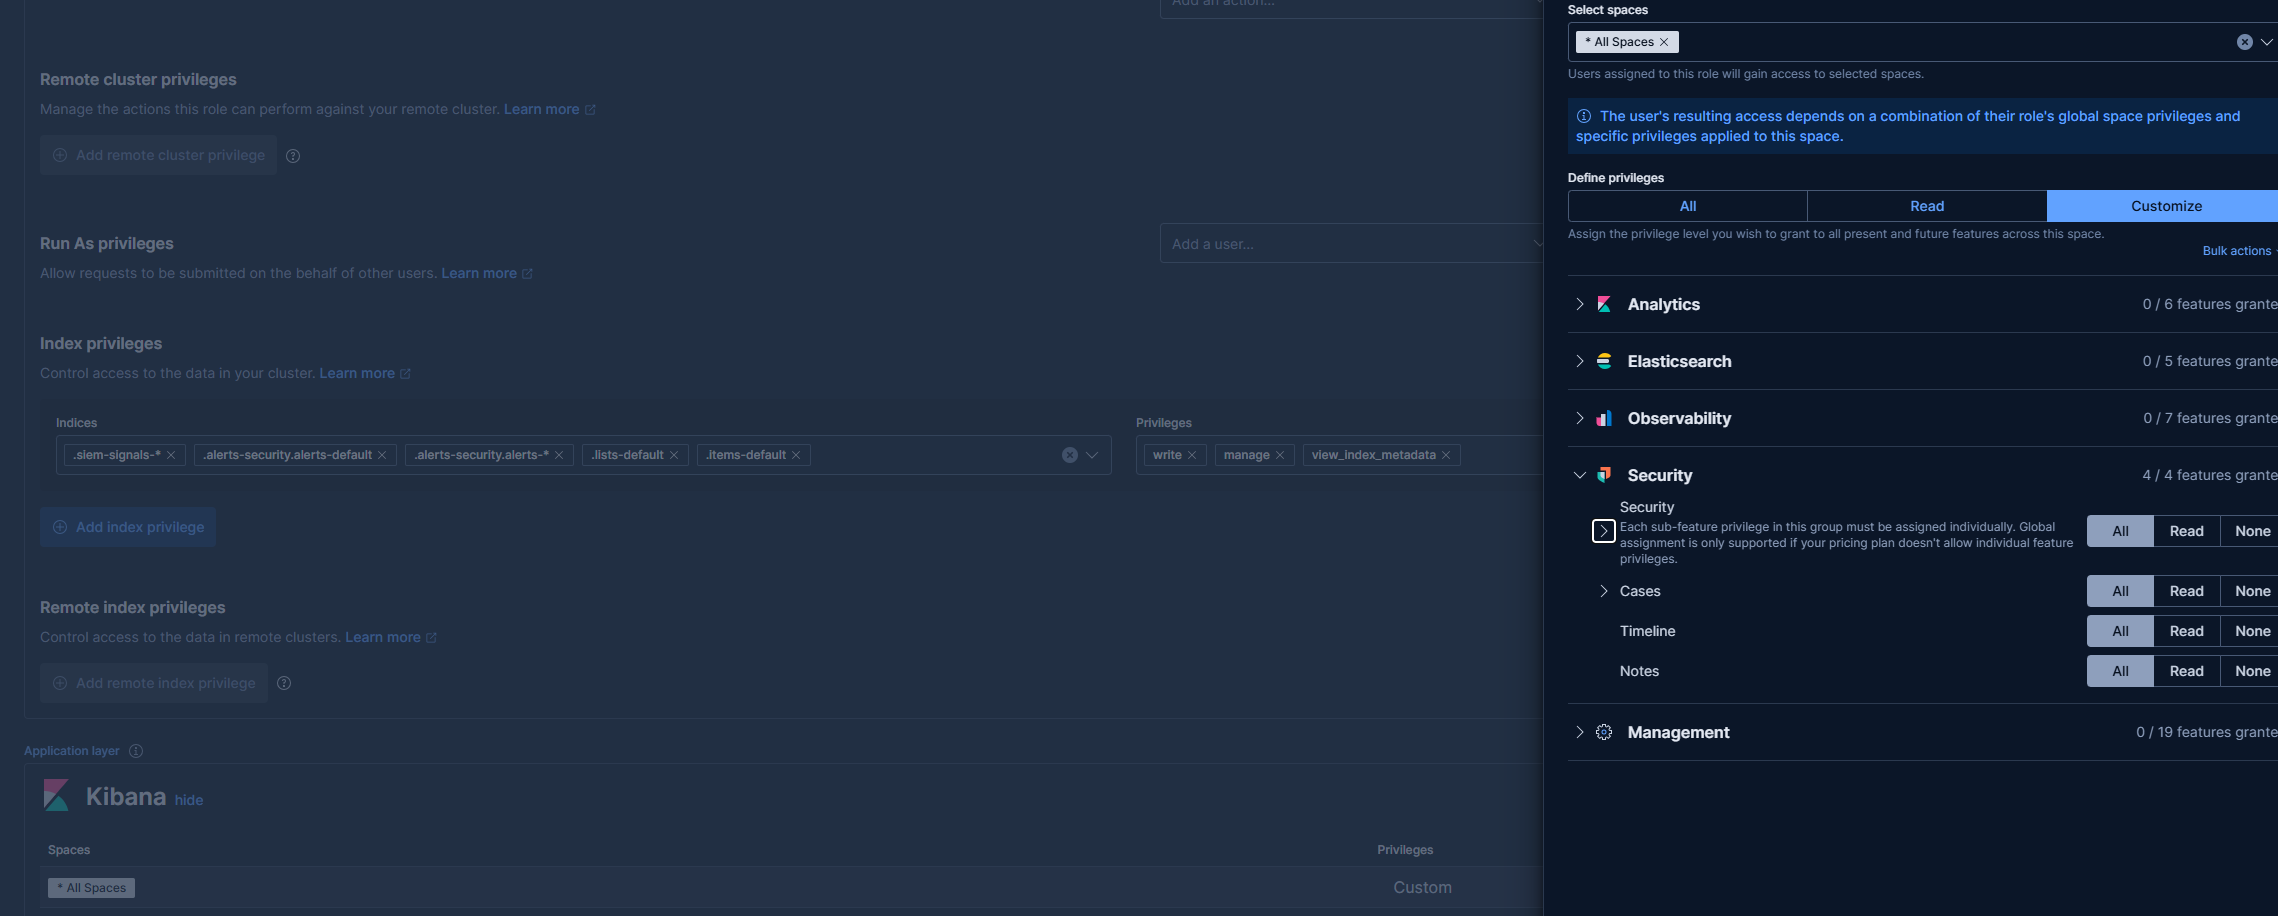
**Posts on this page:** 9
**Page:** 1
### Author:  [@stanley783](https://discuss.elastic.co/u/stanley783)
#### Post date: [October 14, 2025, 3:06pm UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/1 "2025-10-14T15:06:27Z")
Hey there, since kibana 9.1.0 (i think, we upgraded from 8.17.X to 9.1.3), we are unable to edit exception made under SIEM rules. I cant even edit my own exception. Only possible if I have superuser role which is not desired. Me and coworker tried to tinker with permissions separately but were not able to figure it out, even if we gave ouresleves custom “all” permissions for all spaces. (EDIT: and for all indexes/lists)
Is there any way to configure this, in not licensed elk, that we are just missing? Thanks.
---
### Author:  [@williamchan](https://discuss.elastic.co/u/williamchan)
#### Post date: [October 15, 2025, 8:16am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/2 "2025-10-15T08:16:14Z")
Hi @stanley783
In Kibana 9.1.3, editing SIEM rule exceptions is restricted to users with superuser privileges or those who have both:
1. All space privileges for the Security app.
2. Write access to the `.siem-signals-default` index (or your signals index).
Even if you assigned “all” permissions for all spaces, proper index privileges are still required. Check the roles to ensure they include write access to the signals index and rule management. Some users have resolved this by upgrading to a newer Kibana version.
If you use Elastic Cloud, Elastic Cloud Enterprise, or support from companies like Qbox, Webkul or Found, you can contact them for assistance.
---
### Author:  [@stanley783](https://discuss.elastic.co/u/stanley783)
#### Post date: [October 15, 2025, 2:41pm UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/3 "2025-10-15T14:41:14Z")
Hi, thanks for answer. By “all” i meant all reasonable privileges (create, write, manage…) on all possible indexes (various signal and alerts indexes) but still had no luck. Maybe will try upgrading and update later on.
---
### Author:  [@Tortoise](https://discuss.elastic.co/u/Tortoise)
#### Post date: [October 16, 2025, 10:53am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/4 "2025-10-16T10:53:12Z")
Hello @stanley783
As we can see below are the privileges needed to edit the rules which should be assigned to a role :
You need the following privileges to fully access this functionality. Contact your administrator for further assistance.
**Missing Elasticsearch index privileges:**
1. Missing write, view\_index\_metadata, manage privileges for the .items-default data stream. Without these privileges, you cannot create or edit value lists.
2. Missing write, view\_index\_metadata, manage privileges for the .lists-default data stream. Without these privileges, you cannot create or edit value lists.
3. Missing write, view\_index\_metadata, manage privileges for the .alerts-security.alerts-default index.
**Missing Kibana feature privileges:**
1. Missing all privileges for the siemV2 feature. Without that privilege you cannot create or edit detection engine rules.

Thanks!!
---
### Author:  [@stanley783](https://discuss.elastic.co/u/stanley783)
#### Post date: [October 17, 2025, 11:57am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/5 "2025-10-17T11:57:34Z")
Hi, thanks for advice, unfortunately this did not change the situation as well.
---
### Author:  [@stanley783](https://discuss.elastic.co/u/stanley783)
#### Post date: [November 11, 2025, 8:55am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/6 "2025-11-11T08:55:59Z")
just to close this thread, upgrading from 9.1.3 to higher version fixed the issue
---
### Author:  [@michael-a](https://discuss.elastic.co/u/michael-a)
#### Post date: [November 26, 2025, 5:59am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/7 "2025-11-26T05:59:54Z")
Might be an issue with user-defined roles we’ve made, but we have exactly the same issue for a role that prior to upgrading to v9 was able to modify exceptions but now (we’re on 9.1.5) doesn’t - unless you’re a superuser, exceptions can’t be changed.
---
### Author:  [@stanley783](https://discuss.elastic.co/u/stanley783)
#### Post date: [December 9, 2025, 10:01am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/8 "2025-12-09T10:01:36Z")
9.2.0 fixed it so normal roles can edit again. But on 9.1.3, I am not sure if I could edit them even with superuser role on my account, only elastic account could
---
### Author:  [@michael-a](https://discuss.elastic.co/u/michael-a)
#### Post date: [December 10, 2025, 6:25am UTC](https://discuss.elastic.co/t/kibana-9-1-security-rule-exception-edit-not-possible/382710/9 "2025-12-10T06:25:01Z")
Same experience when it comes to fixing it in 9.2 for our regular user role so that’s very welcome, in 9.1.4/5 we could adjust exceptions as any user with superuser role.