# Kibana grok patterns match exact string
**URL:** https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257
**Category:** Kibana
**Tags:** ingest-pipeline
**Created:** [March 24, 2021, 7:38pm UTC](https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257 "2021-03-24T19:38:36Z")
**Posts on this page:** 5
**Page:** 1
### Author:  [@alidrsn](https://discuss.elastic.co/u/alidrsn)
#### Post date: [March 24, 2021, 7:38pm UTC](https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257/1 "2021-03-24T19:38:36Z")
Hello there,
I want to ingest a log with grok patterns in kibana.
The log time format is slightly different from ready-made drafts as belove.
03/24 21:56:55.300 INFO Security.....
Time Format -\> dd/MM hh:mm:ss.SSS
I want to match it with DATA pattern, and i am trying to make a stop point the other field (Log\_Type) which can be INFO,WARN,ERROR
However, i have to also make them(INFO or WARN or ERROR) a field, and i don't know how to do it with regex.
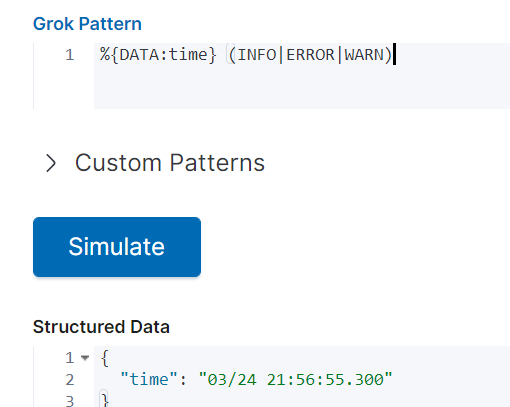
Anyone can help me to fix it ?
Thanks beforehand.
---
### Author:  [@tsullivan](https://discuss.elastic.co/u/tsullivan)
#### Post date: [March 26, 2021, 10:40pm UTC](https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257/2 "2021-03-26T22:40:21Z")
You could define a regular expression to match the Log\_Type:
`%{DATA:time} (?INFO|WARN|ERROR) `
But you shouldn't use a custom regex for this. Take a look at the Grok documentation: [Grok filter plugin | Logstash Reference [7.12] | Elastic](https://www.elastic.co/guide/en/logstash/current/plugins-filters-grok.html)
There is a syntax to Grok expressions, and has about 120 built-in patterns defined here: [logstash-patterns-core/patterns at master · logstash-plugins/logstash-patterns-core · GitHub](https://github.com/logstash-plugins/logstash-patterns-core/tree/master/patterns)
You could use the `LOGLEVEL` pattern to match your `Log_Type` data:
`%{DATA:timestamp} %{LOGLEVEL:level}`
---
### Author:  [@alidrsn](https://discuss.elastic.co/u/alidrsn)
#### Post date: [March 29, 2021, 6:15am UTC](https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257/3 "2021-03-29T06:15:52Z")
Hi @tsullivan ,
%{DATA:time} is not exactly what i trying to do. Because, there is one space between date and time. time field will be '03/24'. However, i want to make it all '03/24 21:56.55.300'.
I figured it out by writing custom regex as you mentioned. Just wanna now if it is possible without regex.
Regards,
---
### Author:  [@tsullivan](https://discuss.elastic.co/u/tsullivan)
#### Post date: [March 29, 2021, 4:26pm UTC](https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257/4 "2021-03-29T16:26:48Z")
Hi, you can use "custom patterns" to create a new pattern by composing built-in patterns. [Grok filter plugin | Logstash Reference [7.12] | Elastic](https://www.elastic.co/guide/en/logstash/current/plugins-filters-grok.html#_custom_patterns)
A custom pattern that can match `03/24 21:56:55.300` as a timestamp would look like:
`ALIDRSN_DATE %{MONTHNUM}/%{MONTHDAY} %{TIME}`
In the Grok Pattern, you use the custom pattern as:
`%{ALIDRSN_DATE:date} %{LOGLEVEL:level} %{GREEDYDATA:msg}`
The resulting structured data would look like:
```auto
{
"date": "03/24 21:56:55.300",
"msg": "Security.....",
"level": "INFO"
}
```
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [April 26, 2021, 4:27pm UTC](https://discuss.elastic.co/t/kibana-grok-patterns-match-exact-string/268257/5 "2021-04-26T16:27:09Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.