# KV Filter Regex
**URL:** https://discuss.elastic.co/t/kv-filter-regex/266730
**Category:** Logstash
**Created:** [March 9, 2021, 5:53pm UTC](https://discuss.elastic.co/t/kv-filter-regex/266730 "2021-03-09T17:53:05Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@lumi](https://discuss.elastic.co/u/lumi)
#### Post date: [March 9, 2021, 5:53pm UTC](https://discuss.elastic.co/t/kv-filter-regex/266730/1 "2021-03-09T17:53:06Z")
Hello
I have the following message getting from Qradar: ( I have changed some things like ID, logon etc...)
```auto
A network share object was accessed. Subject: Security ID: ELK\\test-test$ Account Name: test-test$ Account Domain: ELASTIC Logon ID: xxxxxx Network Information: Object Type: File Source Address: 8.8.8.8 Source Port: 88888 Share Information: Share Name: \\\\*\\IPC$ Share Path: Access Request Information: Access Mask: 0x1 Accesses: ReadData (or ListDirectory)
```
I wanted to use KV Filter to see create Key values automatically
This is my config for key Value
```auto
kv{
source => "Message"
field_split => "((?:[A-Za-z0-9_-] ?)+): +([^]*?) " value_split => ":"
}
```
Unfortunately it doesn't set write it in the index.
I tested my Regex. It should be working.
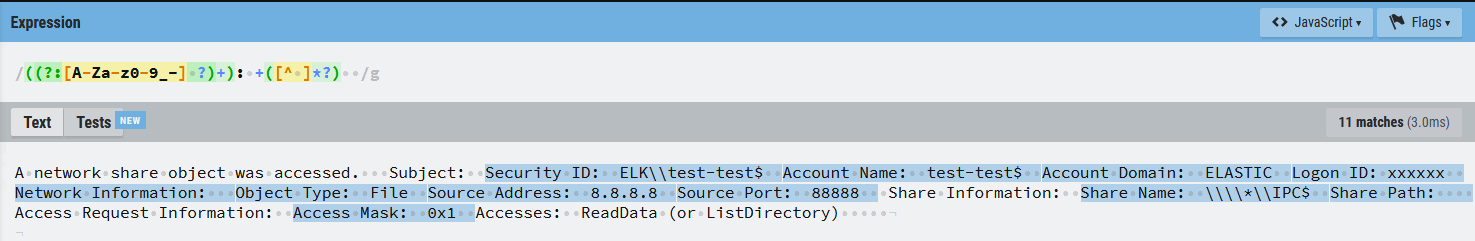
Now i've tried the new feature **Ingest Node Pipelines**. There i can see an error with no information.

Can anybody help me?
---
### Author:  [@Badger](https://discuss.elastic.co/u/Badger)
#### Post date: [March 9, 2021, 6:13pm UTC](https://discuss.elastic.co/t/kv-filter-regex/266730/2 "2021-03-09T18:13:28Z")
> [@lumi](#):
>
> `field_split => "((?:[A-Za-z0-9_-] ?)+): +([^]*?) "`
At a minimum, this should be changed to use [field\_split\_pattern](https://www.elastic.co/guide/en/logstash/current/plugins-filters-kv.html#plugins-filters-kv-field_split_pattern) instead of field\_split.
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [April 6, 2021, 6:14pm UTC](https://discuss.elastic.co/t/kv-filter-regex/266730/3 "2021-04-06T18:14:27Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.