# Logstsh parce grok add teg \_grokparsefailure
**URL:** https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251
**Category:** Logstash
**Created:** [February 15, 2022, 1:55pm UTC](https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251 "2022-02-15T13:55:26Z")
**Posts on this page:** 5
**Page:** 1
### Author:  [@bsilsy](https://discuss.elastic.co/u/bsilsy)
#### Post date: [February 15, 2022, 1:55pm UTC](https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251/1 "2022-02-15T13:55:26Z")
good day everyone!
I'm trying to parse field "message" with grock but, i get \_grokparsefailure tag on 100% of documents
send data using filebeat
message log example
```auto
"message": "10.10.10.10 - text [15/Feb/2022:15:27:27 +0300] 0.170 \"POST /text/ HTTP/1.1\" 200 735 \"-\" \"-\" \"text\" \"-\" \"-\" \"text\" \"111111111111\" \"text\""
```
my conf pipeline
```auto
input {
beats {
host => "0.0.0.0"
port => 5044
}
}
filter {
grok {
match => { "message" => "%{IPV4:ip} - %{WORD:text1} \[%{HTTPDATE:timestamp}\] %{NUMBER:duration} \\"%{WORD:text2} \/%{WORD:text3}/ HTTP/%{NUMBER:httpversion} *?%{DATA:rawrequest} %{NUMBER:response} %{NUMBER:bytes} \\"-\\" \\"-\\" \\"%{WORD:text4}\\" \\"-\\" \\"-\\" \\"%{WORD:text5}\\" \\"%{NUMBER:id}\\" \\"%{WORD:text5}\\"" }
}
}
output {
elasticsearch {
hosts => "localhost:9200"
index => "myindex-%{+YYYY.MM.dd}"
}
}
```
it is working at grok debugger

i need any help, thanks!
---
### Author:  [@Badger](https://discuss.elastic.co/u/Badger)
#### Post date: [February 15, 2022, 5:24pm UTC](https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251/2 "2022-02-15T17:24:56Z")
Try
```
grok { match => { "message" => '%{IPV4:ip} - %{WORD:text1} \[%{HTTPDATE:timestamp}\] %{NUMBER:duration} "%{WORD:text2} \/%{WORD:text3}/ HTTP/%{NUMBER:httpversion}" *?%{DATA:rawrequest} %{NUMBER:response} %{NUMBER:bytes} "-" "-" "%{WORD:text4}" "-" "-" "%{WORD:text5}" "%{NUMBER:id}" "%{WORD:text5}"' } }
```
Note that you have two [text5] fields.
---
### Author:  [@bsilsy](https://discuss.elastic.co/u/bsilsy)
#### Post date: [February 16, 2022, 5:52am UTC](https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251/3 "2022-02-16T05:52:55Z")
> [@Badger](#):
>
> Note that you have two [text5] fields.
I renamed one of the Text5 fields
I tried changing the " to ' as you indicated, but it didn't help. I also get get \_grokparsefailure tag on 100% of documents.

if I add to the filter, if [event][module] == "nginx", then I get 50-60% \_grokparsefailure tag, but the fields I need are not visible.

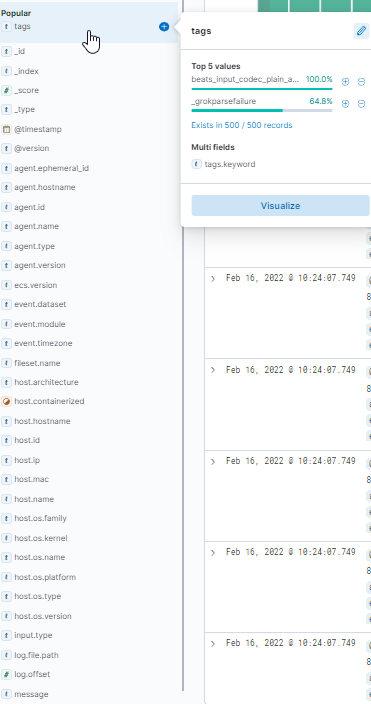
I apologize for not the best screenshots
in the log I get
```auto
[logstash.outputs.elasticsearch] Using a default mapping template {:es_version=>7, :ecs_compatibility=>:disabled}
```
tried adding a string to output, but it didn't change anything
```auto
ecs_compatibility => "v1"
```
---
### Author:  [@Badger](https://discuss.elastic.co/u/Badger)
#### Post date: [February 16, 2022, 6:30pm UTC](https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251/4 "2022-02-16T18:30:27Z")
If your grok is not matching then see [here](https://discuss.elastic.co/t/use-grok-to-filter-mysql-slow-queries/169248/2), also [here](https://discuss.elastic.co/t/grokking-works-in-debugger-but-differs-in-logstash/196793/2).
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [March 16, 2022, 6:30pm UTC](https://discuss.elastic.co/t/logstsh-parce-grok-add-teg-grokparsefailure/297251/5 "2022-03-16T18:30:32Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.