# Manual certificate configuratio for fleet-server and elastic-agent
**URL:** https://discuss.elastic.co/t/manual-certificate-configuratio-for-fleet-server-and-elastic-agent/378071
**Category:** Elasticsearch
**Tags:** fleet
**Created:** [May 13, 2025, 4:07am UTC](https://discuss.elastic.co/t/manual-certificate-configuratio-for-fleet-server-and-elastic-agent/378071 "2025-05-13T04:07:34Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@jack\_a](https://discuss.elastic.co/u/jack_a)
#### Post date: [May 13, 2025, 4:07am UTC](https://discuss.elastic.co/t/manual-certificate-configuratio-for-fleet-server-and-elastic-agent/378071/1 "2025-05-13T04:07:34Z")
I have a cluster and i was trying to add a fleet-server and then enroll one elastic-agent but i kinda stuck and could not make it work. I read the documentation and i have some questions which is not clear so i though i could find some answers here. First Lets star with what i have done. I have tried to follow [One-way and mutual TLS certifications flow](https://www.elastic.co/docs/reference/fleet/tls-overview) and [Elastic Agent command reference](https://www.elastic.co/docs/reference/fleet/agent-command-reference#elastic-agent-diagnostics-command) but i could not make it work.
My understanding is as follow:
**A: fleet-server configuration** :
1. fleet-server \<-\> es
- `--fleet-server-es-ca` : CA which validates certificate represented by ES.
- `--fleet-server-es-cert` : cert which fleet server will represent to ES.
- `--fleet-server-es-cert-key` : the key of `--fleet-server-es-cert`.
- `fleet-server-client-auth` : how to verify cert represented by ES. default is `none`.
- `--certificate-authorities` : CA which validates certificate represented by elastic-agent.
- `--fleet-server-cert` : cert which fleet server will represent to elastic-agent.
- `--fleet-server-cert-key` : the key of `--fleet-server-cert`.
- `--fleet-server-cert-key-passphrase` : the pass of `--fleet-server-cert-key`.
**B: elastic-agent**
1. elastic-agent \<-\> fleet-server
- `--certificate-authorities` : CA which validates certificate represented by elastic-server.
- `--elastic-agent-cert` : certificate which elastic-agent with represent to elastic-server.
- `--elastic-agent-cert-key` : the key of `--elastic-agent-cert`.
- `--elastic-agent-cert-key-passphrase` : the pass of `--elastic-agent-cert-key`
Question on section A-1, why there is no configuration for key passphraese for the `--fleet-server-es-cert-key`? I guess it means when using PEM fomrat and not keystore the key can not have a password?
Question on section A-1, Does the `fleet-server-client-auth` specify how to validate recieved certificate from both ES and elastic-agent?

Question: In the picture above why the `--certificate-authorities` have two values : `fleet-ca, agent-ca` . Just a TYPO?!
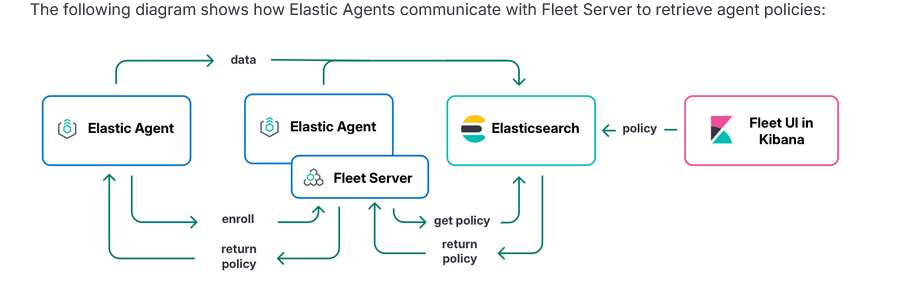
Question: The elastic agent itself is directly connected to elasticsearch, what are the prameters to secure that connection?
Question: if fleet-server is some sort of elastic-agent with some extra features, it does not mean if i want for example user `system` integration on my fleet-server i have to set section B-1 parameters for the fleet-server?
I gues i have to say it is not clear for me what set of parmaters to be set on each fleet-server and elastic-agent to sercure, fleet-server \<-\> es, fleet-server \<-\> elastic-agent, elastic-agnet \<-\> es. The naming is a bit confusing.

also in the output setting three is a `trusted_ca_finger_print` section what is the relation between that and `--fleet-server-es-ca` or `--fleet-server-es-ca-trusted-fingerprint`, what happens when both configuration is set? one in the output section and a different one ( `--fleet-server-es-ca` or `--fleet-server-es-ca-trusted-fingerprint`) while running `install` command?
---
### Author:  [@MichelLaterman](https://discuss.elastic.co/u/MichelLaterman)
#### Post date: [June 12, 2025, 3:01pm UTC](https://discuss.elastic.co/t/manual-certificate-configuratio-for-fleet-server-and-elastic-agent/378071/2 "2025-06-12T15:01:48Z")
> [@jack\_a](#):
>
> Question on section A-1, why there is no configuration for key passphraese for the `--fleet-server-es-cert-key`? I guess it means when using PEM fomrat and not keystore the key can not have a password?
That's an oversight on our part, there is no flag to specify a fleet-server-es-key-passphrase. Please make an issue in the elastic-agent repo for this
> [@jack\_a](#):
>
> Does the `fleet-server-client-auth` specify how to validate recieved certificate from both ES and elastic-agent?
Your initial understanding was incorrect. This options only controls fleet-server's client auth approach to agents as clients. If it's set to required, every connecting agent needs a cert+key.
> [@jack\_a](#):
>
> Question: In the picture above why the `--certificate-authorities` have two values : `fleet-ca, agent-ca` . Just a TYPO?!
This is a comma separated list for paths; it's specifying the CA fleet-server uses to validate connections it makes (`fleet-ca`) and the certificates that agents present to it `agent-ca`.
You can pass a single CA bundle, or paths to multiple CAs
> [@jack\_a](#):
>
> Question: The elastic agent itself is directly connected to elasticsearch, what are the prameters to secure that connection?
These can be found in the UI, under the elasticsearch output settings in fleet: [Elasticsearch output settings | Elastic Docs](https://www.elastic.co/docs/reference/fleet/es-output-settings)
> [@jack\_a](#):
>
> Question: if fleet-server is some sort of elastic-agent with some extra features, it does not mean if i want for example user `system` integration on my fleet-server i have to set section B-1 parameters for the fleet-server?
Almost, you only need to specify `--elastic-agent-cert` if you have set `--fleet-server-client-auth` to required. And you only need `--certificate-authorities` when you're using a custom CA for ES or `--fleet-server-cert`
---
### Author:  [@jack\_a](https://discuss.elastic.co/u/jack_a)
#### Post date: [July 9, 2025, 10:41am UTC](https://discuss.elastic.co/t/manual-certificate-configuratio-for-fleet-server-and-elastic-agent/378071/3 "2025-07-09T10:41:51Z")
The second picture is wrong and this is the right picture:
