# Role based access
**URL:** https://discuss.elastic.co/t/role-based-access/26873
**Category:** Elasticsearch
**Tags:** elastic-stack-security
**Created:** [August 5, 2015, 9:48am UTC](https://discuss.elastic.co/t/role-based-access/26873 "2015-08-05T09:48:14Z")
**Posts on this page:** 11
**Page:** 1
### Author:  [@Jason\_Zheng](https://discuss.elastic.co/u/Jason_Zheng)
#### Post date: [August 5, 2015, 9:48am UTC](https://discuss.elastic.co/t/role-based-access/26873/1 "2015-08-05T09:48:14Z")
Hi All,
I would like to have different privilege for different user in using Kibana, I added user by
> $/usr/share/elasticsearch/bin/shield/esusers useradd franky -r kibana4\_monitoring -p password
and then modify roles.yml, first I mark indices lines of kibana4 and add kibana4\_monitoring as following (each elasticsearch node)
```
kibana4:
cluster:
- cluster:monitor/nodes/info
- cluster:monitor/health
indices:
# '*':
# - indices:admin/mappings/fields/get
# - indices:admin/validate/query
# - indices:data/read/search
# - indices:data/read/msearch
# - indices:admin/get
'.kibana':
- indices:admin/exists
- indices:admin/mapping/put
- indices:admin/mappings/fields/get
- indices:admin/refresh
- indices:admin/validate/query
- indices:data/read/get
- indices:data/read/mget
- indices:data/read/search
- indices:data/write/delete
- indices:data/write/index
- indices:data/write/update
- indices:admin/create
kibana4_monitoring:
cluster:
- cluster:monitor/nodes/info
- cluster:monitor/health
indices:
# 'logstash-*':
# - indices:admin/mappings/fields/get
# - indices:admin/validate/query
# - indices:data/read/search
# - indices:data/read/msearch
# - indices:admin/get
'franky-*':
- indices:read
'.kibana':
- indices:admin/create
- indices:admin/exists
- indices:admin/mapping/put
- indices:admin/mappings/fields/get
- indices:admin/refresh
- indices:admin/validate/query
- indices:data/read/get
- indices:data/read/mget
- indices:data/read/search
- indices:data/write/delete
- indices:data/write/index
- indices:data/write/update
```
then add franky to group kibana4\_monitoring
```
$/usr/share/elasticsearch/bin/shield/esusers roles franky -a kibana4_monitoring
```
finally, I modified kibana.yml as following and restart kibana
```
kibana_elasticsearch_username: franky
kibana_elasticsearch_password: password
```
But the user franky still can use logstash-\* index to do discover, visualize or dashboard, it seems not correct, I purpose the user franky only can use franky-\* index, any one have idea

---
### Author:  [@Jason\_Zheng](https://discuss.elastic.co/u/Jason_Zheng)
#### Post date: [August 6, 2015, 6:49am UTC](https://discuss.elastic.co/t/role-based-access/26873/2 "2015-08-06T06:49:53Z")
Anyone have idea?
---
### Author:  [@pranavburnwal](https://discuss.elastic.co/u/pranavburnwal)
#### Post date: [August 6, 2015, 9:46am UTC](https://discuss.elastic.co/t/role-based-access/26873/3 "2015-08-06T09:46:18Z")
Hi Jason,
Actually the feature you request is called role based access.
To use you have to create a role for the particular index and then assign `franky` that role.
Use this link from shield documentation: [Here](https://www.elastic.co/guide/en/shield/current/configuring-rbac.html)
If you still face problem, reply here. 👍
Pranav
---
### Author:  [@Jason\_Zheng](https://discuss.elastic.co/u/Jason_Zheng)
#### Post date: [August 7, 2015, 9:12am UTC](https://discuss.elastic.co/t/role-based-access/26873/5 "2015-08-07T09:12:44Z")
Hi Pranav,
I list the user franky privilege
```
[root@elasticsearch ~]# /usr/share/elasticsearch/bin/shield/esusers list franky
franky : kibana4_monitoring,kibana4
```
roles.yml (master and nodes)
```
kibana4:
cluster:
- cluster:monitor/nodes/info
- cluster:monitor/health
indices:
# '*':
# - indices:admin/mappings/fields/get
# - indices:admin/validate/query
# - indices:data/read/search
# - indices:data/read/msearch
# - indices:admin/get
'.kibana':
- indices:admin/exists
- indices:admin/mapping/put
- indices:admin/mappings/fields/get
- indices:admin/refresh
- indices:admin/validate/query
- indices:data/read/get
- indices:data/read/mget
- indices:data/read/search
- indices:data/write/delete
- indices:data/write/index
- indices:data/write/update
- indices:admin/create
kibana4_server:
cluster:
- cluster:monitor/nodes/info
- cluster:monitor/health
indices:
'.kibana':
- indices:admin/exists
- indices:admin/mapping/put
- indices:admin/mappings/fields/get
- indices:admin/refresh
- indices:admin/validate/query
- indices:data/read/get
- indices:data/read/mget
- indices:data/read/search
- indices:data/write/delete
- indices:data/write/index
- indices:data/write/update
kibana4_monitoring:
cluster:
- cluster:monitor/nodes/info
- cluster:monitor/health
indices:
# 'logstash-*':
# - indices:admin/mappings/fields/get
# - indices:admin/validate/query
# - indices:data/read/search
# - indices:data/read/msearch
# - indices:admin/get
'franky-*':
- indices:read
'.kibana':
- indices:admin/create
- indices:admin/exists
- indices:admin/mapping/put
- indices:admin/mappings/fields/get
- indices:admin/refresh
- indices:admin/validate/query
- indices:data/read/get
- indices:data/read/mget
- indices:data/read/search
- indices:data/write/delete
- indices:data/write/index
- indices:data/write/update
```
then restart elasticsearch service (master and node)
Kibana.yml setting
```
kibana_elasticsearch_username: franky
kibana_elasticsearch_password: password
```
But franky still can operate 'logstash-_', franky should only operate 'franky-_'

My purpose is according to [https://www.elastic.co/guide/en/shield/current/kibana.html#using-kibana4-with-shield](https://www.elastic.co/guide/en/shield/current/kibana.html#using-kibana4-with-shield) steps

Jason
---
### Author:  [@pranavburnwal](https://discuss.elastic.co/u/pranavburnwal)
#### Post date: [August 10, 2015, 6:01am UTC](https://discuss.elastic.co/t/role-based-access/26873/6 "2015-08-10T06:01:46Z")
Hey,
So In place of `logstash-*` you have to replace it with `franky-*` not comment it.
---
### Author:  [@Jason\_Zheng](https://discuss.elastic.co/u/Jason_Zheng)
#### Post date: [August 11, 2015, 2:16am UTC](https://discuss.elastic.co/t/role-based-access/26873/7 "2015-08-11T02:16:15Z")
Hi Pranav,
As you said, I did replace logstash-\* to franky-\*, and restart all services (elasticsearch, kibana), it can be work normally, thanks
I do not understand, why does it not work as following syntax?
```
'franky-*':
- indices:read
```
BTW, when I first time visit kibana, the dialog popup to ask me enter account and password, my question is how to logout kibana with sheild?
Jason
---
### Author:  [@pranavburnwal](https://discuss.elastic.co/u/pranavburnwal)
#### Post date: [August 11, 2015, 4:00am UTC](https://discuss.elastic.co/t/role-based-access/26873/8 "2015-08-11T04:00:15Z")
Hi,
I guess you have not been through all the documentation of shield.
> indices:read
is not valid.
Please find the valid cluster and indices action privileges here: [Here](https://www.elastic.co/guide/en/shield/current/reference.html#ref-actions-list)
---
### Author:  [@skearns](https://discuss.elastic.co/u/skearns)
#### Post date: [August 11, 2015, 10:30am UTC](https://discuss.elastic.co/t/role-based-access/26873/9 "2015-08-11T10:30:40Z")
Hi Jason,
I'm glad that Pranav's help has things working the way you want (thanks Pranav!)
Today, when using Shield, Kibana will prompt you for your username/password. This uses the browser's built-in HTTP Basic Auth support, which caches your credentials after a successful authentication. For now, the only way to log out is to close the browser.
That said, we are already working on full session support with login/logout, and I believe this is planned for the next version of Kibana: [https://github.com/elastic/kibana/issues/3904](https://github.com/elastic/kibana/issues/3904)
Thanks,
Steve
---
### Author:  [@Jason\_Zheng](https://discuss.elastic.co/u/Jason_Zheng)
#### Post date: [August 17, 2015, 1:54am UTC](https://discuss.elastic.co/t/role-based-access/26873/10 "2015-08-17T01:54:17Z")
Hi Steve,
Thanks for replying,
Another question, (kibana within shield)
User A login Kibana, and create 'logstash-_' index pattern
User B login Kibana, and create 'franky-_' index pattern
User A allowed to access logstash indices, user B not allowed to access logstash indices, but whatever User A or User B login Kibana, all of index pattern they can see, just only user A can access logstash-_, user B cannot use logstash-_
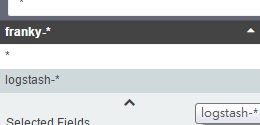
Is it possible to get different view (READ ACL) to User A and B
Jason
---
### Author:  [@skearns](https://discuss.elastic.co/u/skearns)
#### Post date: [August 17, 2015, 12:48pm UTC](https://discuss.elastic.co/t/role-based-access/26873/11 "2015-08-17T12:48:58Z")
Hi Jason,
I'm not sure I understand your question, but I'll try to clarify how things work today. Shield allows you to protect the _data-level_ access at the Elasticsearch layer. Once you have Shield configured, no user will be able to see data from an index they do not have access to.
In Kibana, we do not yet have the ability to isolate individual dashboards/saved searches/visualizations or index mappings, so that all users will be able to _see that they exist_ but with Shield, they will not be able to actually see any data they shouldn't.
We are planning to allow Kibana to protect individual objects, but this is something we're still working on.
I hope that helps.
Thanks,
Steve
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [July 6, 2017, 1:48pm UTC](https://discuss.elastic.co/t/role-based-access/26873/12 "2017-07-06T13:48:34Z")