# Sending Metricbeat Logs directly to Elasticsearch
**URL:** https://discuss.elastic.co/t/sending-metricbeat-logs-directly-to-elasticsearch/95828
**Category:** Elasticsearch
**Created:** [August 4, 2017, 7:17am UTC](https://discuss.elastic.co/t/sending-metricbeat-logs-directly-to-elasticsearch/95828 "2017-08-04T07:17:34Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@shrikantgulia](https://discuss.elastic.co/u/shrikantgulia)
#### Post date: [August 4, 2017, 7:17am UTC](https://discuss.elastic.co/t/sending-metricbeat-logs-directly-to-elasticsearch/95828/1 "2017-08-04T07:17:34Z")
I am having two Systems (System1 & System2).
I am unable to collect metricbeat logs of System2 in the Elasticsearch of System1.
My metricbeat.yml file configuration is as below
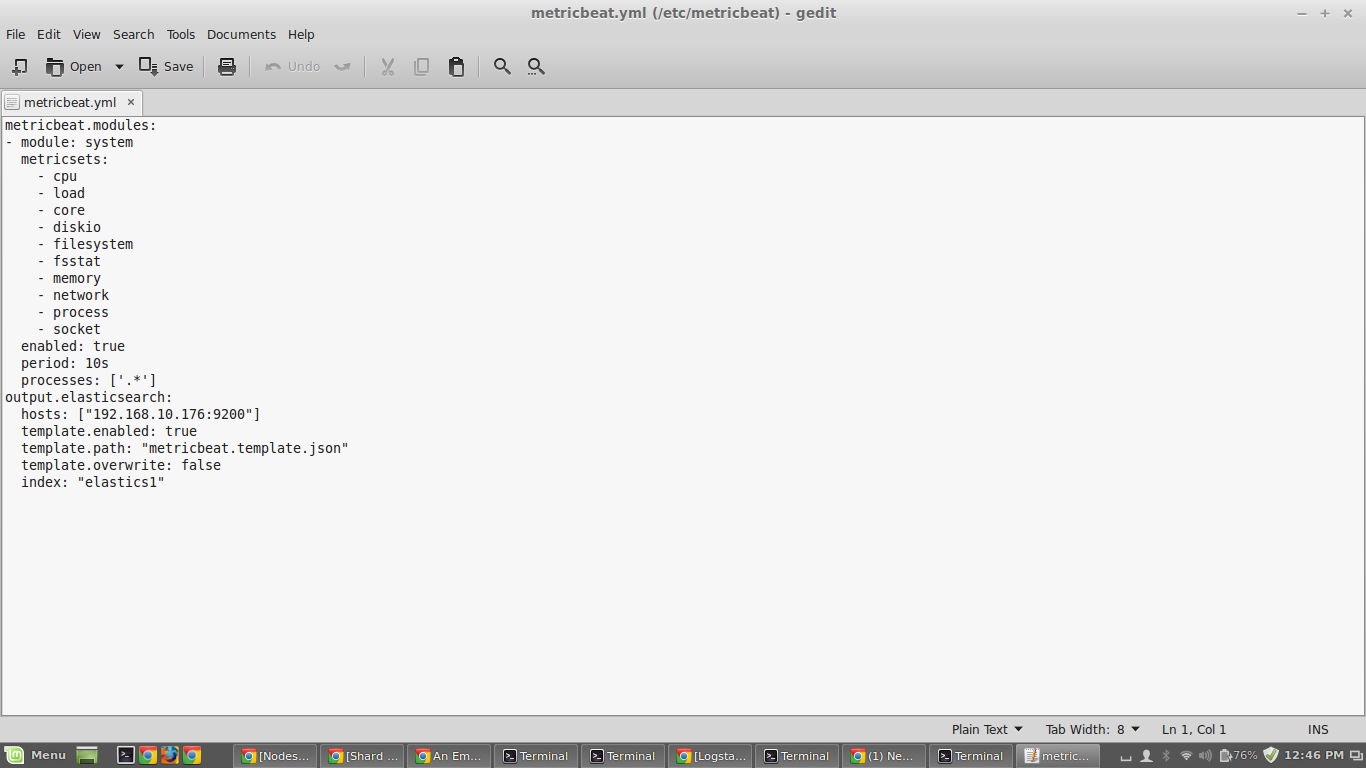
Help would be really appreciated
Thanks
---
### Author:  [@danielmitterdorfer](https://discuss.elastic.co/u/danielmitterdorfer)
#### Post date: [August 11, 2017, 6:48am UTC](https://discuss.elastic.co/t/sending-metricbeat-logs-directly-to-elasticsearch/95828/2 "2017-08-11T06:48:48Z")
Hi @shrikantgulia,
In general I think that question is better suited for the #beats:metricbeat forum but maybe I'm able to give some pointers.
> [@shrikantgulia](#):
>
> I am unable to collect metricbeat logs of System2 in the Elasticsearch of System1.
What do you mean by that? Is 192.168.10.176 reachable from System2 (ping)? Is Elasticsearch bound to `0.0.0.0` instead of loopback? What happens if you issue `curl http://192.168.10.176:9200/`? If you don't see anything like this:
```auto
{
"name" : "OSjLgO2",
"cluster_name" : "elasticsearch",
"cluster_uuid" : "-IZx01UcSkiYc4aj_7Ky_w",
"version" : {
"number" : "5.5.0",
"build_hash" : "260387d",
"build_date" : "2017-06-30T23:16:05.735Z",
"build_snapshot" : false,
"lucene_version" : "6.6.0"
},
"tagline" : "You Know, for Search"
}
```
Then check `config/elasticsearch.yml`, specifically `network.host`. It should be set to `0.0.0.0` to listen on all network interfaces (don't forget to restart Elasticsearch if you change the configuration). By default, Elasticsearch only listens on loopback (i.e. 127.0.0.1).
If that does not help, please check the logs of metricbeat and Elasticsearch for further hints.
Daniel
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [September 8, 2017, 6:48am UTC](https://discuss.elastic.co/t/sending-metricbeat-logs-directly-to-elasticsearch/95828/3 "2017-09-08T06:48:52Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.