# Time fields show different time
**URL:** https://discuss.elastic.co/t/time-fields-show-different-time/346651
**Category:** Elasticsearch
**Created:** [November 7, 2023, 7:07pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651 "2023-11-07T19:07:32Z")
**Posts on this page:** 10
**Page:** 1
### Author:  [@juancamiloll](https://discuss.elastic.co/u/juancamiloll)
#### Post date: [November 7, 2023, 7:07pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/1 "2023-11-07T19:07:32Z")
Hello again,
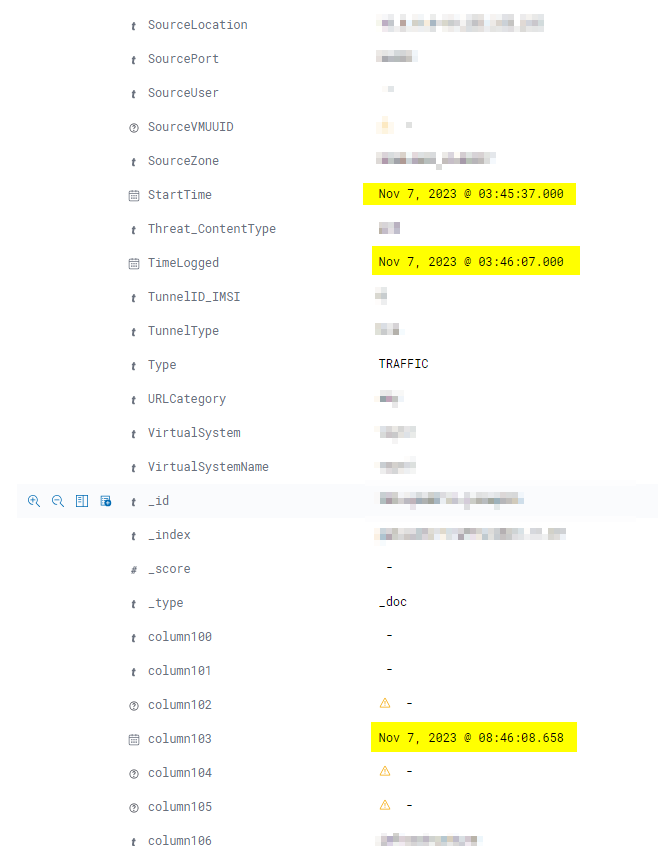
I find a new problem where in the logs of a Paloalto I see that the "ReceivedTime" field and the "column103" field show a different time.
I would appreciate your help
```auto
input {
file {
path => "/opt//system-mypanoramafirewall/2023/11/*/user.log"
exclude => "*.gz"
start_position => "beginning"
tags => ["PAN-OS_SysLog"]
}
}
filter {
if "PAN-OS_SysLog" in [tags] {
# Log types are "TRAFFIC", "THREAT", "CONFIG" and "SYSTEM". URL & Wildfire logs are inside Threat logs
# Log fields: https://www.paloaltonetworks.com/documentation/80/pan-os/pan-os/monitoring/syslog-field-descriptions
if ([message] =~ /TRAFFIC/) {
csv {
source => "message"
columns => [
"FUTURE_USE", "ReceiveTime", "SerialNumber", "Type", "Threat_ContentType", "FUTURE_USE",
"GeneratedTime", "SourceIP", "DestinationIP", "NATSourceIP", "NATDestinationIP", "RuleName",
"SourceUser", "DestinationUser", "Application", "VirtualSystem", "SourceZone", "DestinationZone",
"InboundInterface", "OutboundInterface", "LogForwardingProfile", "TimeLogged", "SessionID",
"RepeatCount", "SourcePort", "DestinationPort", "NATSourcePort", "NATDestinationPort", "Flags",
"Protocol", "Action", "Bytes", "BytesSent", "BytesReceived", "Packets", "StartTime", "ElapsedTime",
"URLCategory", "FUTURE_USE", "SequenceNumber", "ActionFlags", "SourceLocation",
"DestinationLocation", "FUTURE_USE", "PacketsSent", "PacketsReceived", "SessionEndReason",
"DeviceGroupHierarchyLevel1", "DeviceGroupHierarchyLevel2", "DeviceGroupHierarchyLevel3",
"DeviceGroupHierarchyLevel4", "VirtualSystemName", "DeviceName", "ActionSource", "SourceVMUUID",
"DestinationVMUUID", "TunnelID_IMSI", "MonitorTag_IMEI", "ParentSessionID", "ParentStartTime",
"TunnelType"
]
}
mutate {
convert => ["Bytes", "integer"]
convert => ["BytesReceived", "integer"]
convert => ["BytesSent", "integer"]
convert => ["ElapsedTime", "integer"]
convert => ["GeoIP.dma_code", "integer"]
convert => ["GeoIP.latitude", "float"]
convert => ["GeoIP.longitude", "float"]
convert => ["NATDestinationPort", "integer"]
convert => ["NATSourcePort", "integer"]
convert => ["Packets", "integer"]
convert => ["PacketsReceived", "integer"]
convert => ["PacketsSent", "integer"]
convert => ["SequenceNumber", "integer"]
replace => ["host", "%{DeviceName}"]
add_tag => ["PAN-OS_Traffic"]
remove_field => ["message"]
remove_field => ["column108"]
remove_field => ["ParentStartTime"]
}
# ruby {
# code => "event['GeneratedTime'] = event['GeneratedTime'].localtime('+08:00')"
# }
}
else if ([message] =~ /THREAT/) {
csv {
source => "message"
columns => [
"FUTURE_USE", "receive_time", "serial_number", "type", "threat_category", "version",
"GeneratedTime", "src_ip", "dest_ip", "src_translated_ip", "dest_translated_ip", "rule",
"src_user", "dest_ser", "application", "virtual_system", "src_zone", "dest_zone",
"src_interface", "dest_interface", "LogForwardingProfile", "FUTURE_USE", "session_id",
"repeat_count", "source_port", "dest_port", "src_translated_port", "dest_translated_port", "session_flags",
"protocol", "vendor_action", "misc", "threat", "raw_category", "severity", "direction",
"sequence_number", "action_flags", "client_location", "dest_location", "FUTURE_USE",
"ContentType", "pcap_id", "file_digest", "Cloud", "url_index", "user_agent", "file_type",
"X-Forwarded-For", "referer", "sender", "subject", "recipient", "FUTURE_USE",
"DeviceGroupHierarchyLevel1", "DeviceGroupHierarchyLevel2", "DeviceGroupHierarchyLevel3",
"DeviceGroupHierarchyLevel4", "vsys_name", "DeviceName", "FUTURE_USE", "SourceVMUUID",
"DestinationVMUUID", "HTTPMethod", "TunnelID_IMSI", "MonitorTag_IMEI", "ParentSessionID",
"ParentStartTime", "TunnelType", "category", "content_version", "FUTURE_USE", "FUTURE_USE",
"FUTURE_USE", "FUTURE_USE"
]
}
mutate {
convert => ["GeoIP.dma_code", "integer"]
convert => ["GeoIP.latitude", "float"]
convert => ["GeoIP.longitude", "float"]
convert => ["NATDestinationPort", "integer"]
convert => ["NATSourcePort", "integer"]
convert => ["SequenceNumber", "integer"]
replace => ["host", "%{DeviceName}"]
add_tag => ["PAN-OS_Threat"]
remove_field => ["message"]
}
}
else if ([message] =~ /CONFIG/) {
csv {
source => "message"
columns => [
"FUTURE_USE", "ReceiveTime", "Serial_Number", "Type", "Subtype", "FUTURE_USE", "GeneratedTime", "Host",
"Virtual_System", "Command", "Admin", "Client", "Result", "Configuration_Path", "Sequence_Number",
"Action_Flags", "Before_Change_Detail", "After_Change_Detail", "Device Group Hierarchy Level 1",
"Device Group Hierarchy Level 2", "Virtual_System_Name", "DeviceName"
]
}
mutate {
replace => ["host", "%{DeviceName}"]
add_tag => ["PAN-OS_Config"]
remove_field => ["message"]
}
}
else if ([message] =~ /CORRELATION/) {
mutate {
replace => ["host", "%{DeviceName}"]
add_tag => ["PAN-OS_Correlation"]
}
}
else if ([message] =~ /SYSTEM/) {
csv {
source => "message"
columns => [
"FUTURE_USE", "ReceiveTime", "Serial_Number", "Type", "Content/Threat_Type", "FUTURE_USE", "GeneratedTime",
"Virtual_System", "EventID", "Object", "FUTURE_USE", "FUTURE_USE", "Module", "Severity", "Description",
"Sequence_Number", "Action_Flags", "Device Group Hierarchy Level 1", "Device Group Hierarchy Level 2",
"Device Group Hierarchy Level 3", "Device Group Hierarchy Level 4", "Virtual_System_Name", "DeviceName", "Bytes", "By
tes Sent"
]
}
mutate {
replace => ["host", "%{DeviceName}"]
add_tag => ["PAN-OS_System"]
#remove_field => ["message"]
}
}
mutate {
# Original message has been fully parsed, so remove it.
#remove_field => ["message"]
}
# Geolocate logs that have SourceIP if that SourceIP is a non-RFC1918 address
if [SourceIP] and [SourceIP] !~ "(^127\.0\.0\.1)|(^10\.)|(^172\.1[6-9]\.)|(^172\.2[0-9]\.)|(^172\.3[0-1]\.)|(^192\.168\.)|(^169\.
254\.)" {
geoip {
source => "SourceIP"
target => "SourceIPGeo"
}
# Delete 0,0 in SourceIPGeo.location if equal to 0,0
if ([SourceIPGeo.location] and [SourceIPGeo.location] =~ "0,0") {
mutate {
replace => ["SourceIPGeo.location", ""]
}
}
}
# Geolocate logs that have DestinationIP and if that DestinationIP is a non-RFC1918 address
if [DestinationIP] and [DestinationIP] !~ "(^127\.0\.0\.1)|(^10\.)|(^172\.1[6-9]\.)|(^172\.2[0-9]\.)|(^172\.3[0-1]\.)|(^192\.168\
.)|(^169\.254\.)" {
geoip {
source => "DestinationIP"
target => "DestinationIPGeo"
}
# Delete 0,0 in DestinationIPGeo.location if equal to 0,0
if ([DestinationIPGeo.location] and [DestinationIPGeo.location] =~ "0,0") {
mutate {
replace => ["DestinationIPGeo.location", ""]
}
}
}
}
}
output {
if "PAN-OS_SysLog" in [tags] {
elasticsearch {
index => "paloalto-%{+yyyy.MM.dd}"
hosts => ["localhost:9200"]
}
}
}
```
---
### Author:  [@leandrojmp](https://discuss.elastic.co/u/leandrojmp)
#### Post date: [November 7, 2023, 8:46pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/2 "2023-11-07T20:46:46Z")
> [@juancamiloll](#):
>
> I find a new problem where in the logs of a Paloalto I see that the "ReceivedTime" field and the "column103" field show a different time.
Can you share some evidence of this? You just shared your logstash pipeline, not any document that shows what is different.
It is not clear what is different here.
Also, according to the Palo Alto [documentation](https://docs.paloaltonetworks.com/pan-os/11-1/pan-os-admin/monitoring/use-syslog-for-monitoring/syslog-field-descriptions/traffic-log-fields), column 103 would be the _High Resolution Timestamp_ field, which is indeed different from the _Receive Time_ field.
---
### Author:  [@juancamiloll](https://discuss.elastic.co/u/juancamiloll)
#### Post date: [November 7, 2023, 10:07pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/3 "2023-11-07T22:07:56Z")
---
### Author:  [@leandrojmp](https://discuss.elastic.co/u/leandrojmp)
#### Post date: [November 7, 2023, 10:41pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/4 "2023-11-07T22:41:43Z")
In which timezone are you in? This looks like a timezone issue.
---
### Author:  [@juancamiloll](https://discuss.elastic.co/u/juancamiloll)
#### Post date: [November 23, 2023, 9:10pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/5 "2023-11-23T21:10:51Z")
Colombia - Bogotá
---
### Author:  [@leandrojmp](https://discuss.elastic.co/u/leandrojmp)
#### Post date: [November 23, 2023, 10:14pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/6 "2023-11-23T22:14:47Z")
> [@juancamiloll](#):
>
> Colombia - Bogotá
Yeah, this looks like a timezone issue since the difference between the times are 5 hours, which is the difference from Bogotá time to UTC. (UTC-5)
Is the time in your Palo Alto time in UTC or in Bogotá Time?
---
### Author:  [@juancamiloll](https://discuss.elastic.co/u/juancamiloll)
#### Post date: [November 23, 2023, 10:19pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/7 "2023-11-23T22:19:06Z")
In the version I have from ELK I can use the Splunk add-on called "ElasticSplunk" the curious thing is that when I make the query from Splunk to ELK, the "GeneratedTime" and "ReceiveTime" fields are correct, they only appear with time difference when I visualize it from Kibana.
---
### Author:  [@leandrojmp](https://discuss.elastic.co/u/leandrojmp)
#### Post date: [November 23, 2023, 10:22pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/8 "2023-11-23T22:22:31Z")
> [@juancamiloll](#):
>
> they only appear with time difference when I visualize it from K
Because Kibana converts date time from UTC to your browser timezone.
> [@leandrojmp](#):
>
> Is the time in your Palo Alto time in UTC or in Bogotá Time?
You didn't answer that, if the time in your Palo Alto is in Bogotá time, you need to use a date filter in logstash to inform it, because those two fields do not have any timezone information, and Elasticsearch assumes that every date string is in UTC if it does not have timezone information.
---
### Author:  [@juancamiloll](https://discuss.elastic.co/u/juancamiloll)
#### Post date: [November 23, 2023, 10:25pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/9 "2023-11-23T22:25:01Z")
No soy admin del firewall, lo mas seguro es que la fecha sea la de America Bogotá, pero me quedo tranquilo que los eventos tienen la fecha correcta cuando lo consulto desde Splunk.
Muchas gracias por tu ayuda.
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [December 21, 2023, 10:25pm UTC](https://discuss.elastic.co/t/time-fields-show-different-time/346651/10 "2023-12-21T22:25:26Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.