# Very huge amount of traffic by src IP. How handle it?
**URL:** https://discuss.elastic.co/t/very-huge-amount-of-traffic-by-src-ip-how-handle-it/134584
**Category:** Logstash
**Created:** [June 5, 2018, 9:54am UTC](https://discuss.elastic.co/t/very-huge-amount-of-traffic-by-src-ip-how-handle-it/134584 "2018-06-05T09:54:31Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@Vladimir\_Fomin](https://discuss.elastic.co/u/Vladimir_Fomin)
#### Post date: [June 5, 2018, 9:54am UTC](https://discuss.elastic.co/t/very-huge-amount-of-traffic-by-src-ip-how-handle-it/134584/1 "2018-06-05T09:54:31Z")
I've start NetFlow by using this command `/usr/share/logstash/bin/logstash --modules netflow -M netflow.var.input.udp.port=9966` and it works.
But when I look at overview traffic dashboard I see that some host send huge amount of traffic.
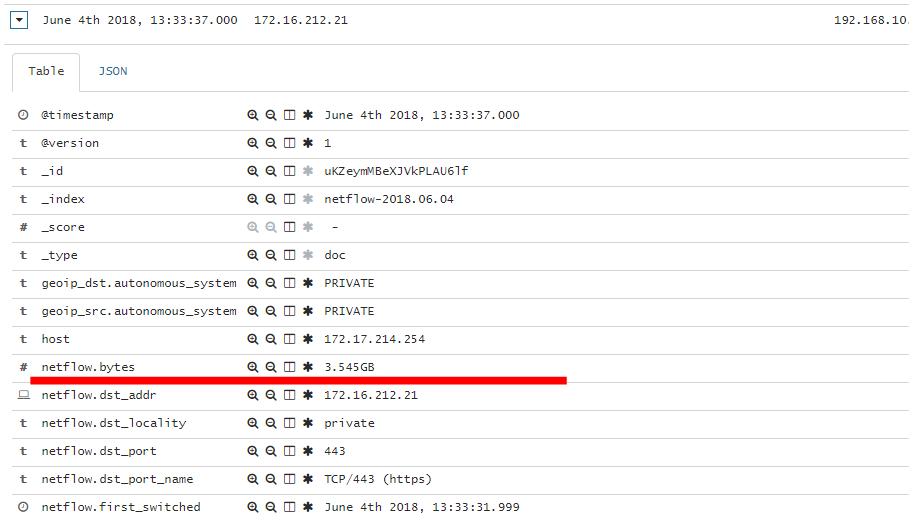
And it's only one packet! We have tons of gigabytes per day for this host.
But in fact this host doesn't send this amount of traffic. Maybe field "netflow.bytes" for this host contains strange invalid value.
Can I configure some filters to discard packets with this strange value?
---
### Author:  [@Magnus\_Kessler](https://discuss.elastic.co/u/Magnus_Kessler)
#### Post date: [June 5, 2018, 10:46am UTC](https://discuss.elastic.co/t/very-huge-amount-of-traffic-by-src-ip-how-handle-it/134584/2 "2018-06-05T10:46:26Z")
Check if you have log entries like shown in [https://github.com/logstash-plugins/logstash-codec-netflow/issues/123](https://github.com/logstash-plugins/logstash-codec-netflow/issues/123).
If yes, try if updating to the latest version of the logstash-codec-netflow plugin resolves the issue.
```auto
bin/logstash-plugin update logstash-codec-netflow
```
I have seen incorrect field values (including netflow.bytes) if the data was interpreted incorrectly due to a misinterpreted netflow template.
---
### Author:  [@system](https://discuss.elastic.co/u/system)
#### Post date: [July 3, 2018, 10:46am UTC](https://discuss.elastic.co/t/very-huge-amount-of-traffic-by-src-ip-how-handle-it/134584/3 "2018-07-03T10:46:32Z")
This topic was automatically closed 28 days after the last reply. New replies are no longer allowed.